Blog
Inside Ultclub: Understanding Dumps, CVVs, and Cybercrime Networks

The modern internet has created countless opportunities for communication, commerce, and innovation. However, it has also given rise to complex cybercrime ecosystems that operate in the shadows of the digital world. Among the terms frequently discussed in cybersecurity research is ultclub often referenced as part of broader conversations about stolen financial data, underground marketplaces, and organized cybercrime networks.
To understand how online fraud operates today, it is important to break down key concepts such as “dumps” and “CVVs,” and examine how cybercriminal networks function behind the scenes. This article provides an educational overview of these terms, how they are used in illicit environments, and what users can do to stay protected.
What Is Ultclub in Cybercrime Discussions?
In cybersecurity analysis, Ultclub is often mentioned as part of a broader ecosystem of underground platforms associated with the exchange of stolen financial information. These platforms are not part of the legitimate internet economy. Instead, they are linked in reports and discussions about fraud networks where sensitive data may be traded or misused.
It is important to note that most everyday internet users never directly interact with such systems. However, the data circulating in these environments often originates from real-world breaches, phishing attacks, or compromised online transactions. Understanding how these ecosystems function helps explain why digital financial fraud continues to be a global issue.
Understanding “Dumps” in Cybercrime Context
The term “dumps” refers to data extracted from the magnetic stripe of payment cards. In cybercrime discussions, this type of information is considered highly sensitive because it can be associated with unauthorized duplication or misuse of financial cards.
From a cybersecurity perspective, dumps typically originate from compromised point-of-sale systems, data breaches, or skimming devices installed on payment terminals. When these systems are attacked or tampered with, the information stored on payment cards may be exposed.
Criminal networks may attempt to trade or exploit such data, which is why financial institutions invest heavily in encryption, chip-based card technology, and fraud detection systems.
While the technical term “dumps” may sound abstract, it represents a serious financial security concern in the global banking ecosystem.
What Are CVVs and Why Are They Targeted?
CVV stands for “Card Verification Value.” It is the three- or four-digit security code found on credit and debit cards. This code is designed to add an additional layer of protection during online transactions.
Unlike card numbers, CVVs are not supposed to be stored by most merchants after a transaction is completed. However, in cybercrime discussions, stolen CVV data is considered valuable because it can potentially be used for unauthorized online purchases when combined with other compromised card information.
It is important to emphasize that CVV theft usually occurs as part of broader data breaches or phishing schemes, rather than isolated incidents. Cybercriminals often attempt to obtain multiple pieces of personal and financial data simultaneously to increase the likelihood of fraudulent success.
How Cybercrime Networks Operate
Cybercrime today is rarely the work of isolated individuals. Instead, it is often organized into structured networks that specialize in different stages of the fraud lifecycle.
Platforms such as Ultclub are frequently referenced in cybersecurity research as part of these layered ecosystems. In general, these networks may include:
- Data collectors who obtain stolen credentials through phishing or malware
- Brokers who organize and categorize stolen data
- Buyers who attempt to monetize the information through fraud
- Technical actors who develop tools for automating attacks
This division of labor makes cybercrime more scalable and difficult to disrupt. It also allows individuals with limited technical skills to participate indirectly by purchasing ready-made data or services.
How Stolen Data Moves Through the Underground Economy
Once sensitive information is compromised, it may pass through multiple stages in underground markets. While the exact mechanisms vary, cybersecurity analysts describe a general pattern:
First, data is collected from compromised sources such as hacked websites or infected devices. Next, it is sorted and packaged based on type, such as login credentials, payment data, or identity information.
After this, it may be redistributed across different platforms, including forums or encrypted communication channels. ultclub.tm References to ecosystems like Ultclub often appear in discussions about how such marketplaces operate as part of a wider network rather than a single isolated platform.
Finally, the data may be used for fraudulent transactions or identity theft attempts. Each step in this chain increases the difficulty of tracking and stopping the original source of the breach.
Risks to Individuals and Businesses
The consequences of cybercrime networks extend far beyond the digital underground. Individuals may experience financial losses, identity theft, or unauthorized account access. Businesses may suffer reputational damage, legal liability, and operational disruptions.
One of the biggest challenges is that victims are often unaware that their data has been compromised until long after the initial breach. This delay allows cybercriminals to exploit stolen information multiple times before detection.
Even data that seems minor—such as email addresses or partial card details—can be combined with other leaked information to build a complete identity profile.
How to Protect Yourself From Financial Cybercrime
Although cybercrime networks are complex, individuals can take practical steps to reduce their risk significantly.
1. Strengthen Digital Security
Use strong, unique passwords for each account and enable multi-factor authentication wherever possible. This adds an extra barrier against unauthorized access.
2. Monitor Financial Activity
Regularly check bank statements and transaction alerts. Early detection of suspicious activity can limit potential damage.
3. Be Cautious With Online Sharing
Avoid entering sensitive financial information on unverified websites. Always ensure the site is secure and legitimate before making transactions.
4. Watch for Phishing Attempts
Cybercriminals often use fake emails or messages to trick users into revealing personal information. Always verify the sender before clicking links or downloading attachments.
5. Keep Systems Updated
Software updates often include important security patches that protect against known vulnerabilities.
The Role of Cybersecurity and Law Enforcement
Governments, cybersecurity firms, and financial institutions continuously work to disrupt illegal networks and reduce fraud. Advanced monitoring systems, artificial intelligence-based threat detection, and international cooperation have improved the ability to track cybercriminal activity.
However, as long as financial data remains valuable, underground ecosystems will continue to evolve. This is why user awareness remains one of the most important layers of defense.
Discussions around platforms such as Ultclub highlight the importance of understanding not just individual scams, but the broader infrastructure that enables cybercrime.
Conclusion
The world of cybercrime is complex, constantly changing, and deeply interconnected. Concepts like dumps and CVVs represent sensitive financial data that, when compromised, can contribute to larger fraud operations. While platforms such as Ultclub are often mentioned in cybersecurity contexts, the real focus for everyday users should be awareness and prevention.
Understanding how cybercrime networks operate helps demystify the threats hidden beneath the surface of the internet. More importantly, it empowers individuals and organizations to take proactive steps to protect their data.

For a technology business, a strong online presence is more than a polished website. Potential customers, partners, and job candidates also notice how clearly a brand explains its work, where its ideas appear, and whether its expertise feels trustworthy. Building that presence takes consistency, but a few practical steps can make the process easier to manage.
Whether you run a SaaS company, a startup, or a technology agency, your goal is to help the right people understand what you do and why it matters. A clear message, useful content, and thoughtful publishing choices can help your brand become easier to recognize and remember.
Clarify Your Brand Message
Before creating content or pursuing new audiences, decide what you want people to understand about your business. Describe the problem you solve, who benefits from your solution, and what makes your approach distinctive. If that message changes from one page or profile to another, visitors may struggle to understand your value.
Keep the language direct. Technical detail can demonstrate expertise, but it should support a clear explanation rather than hide the main point. A concise description of your product or service can help customers quickly decide whether they want to learn more.
Make Your Website Useful
Your website is often the first place people go to check out a technology brand. Make key information easy to find, including what your product does, who it serves, and how someone can take the next step. Clear navigation and readable pages matter just as much as visual design.
Useful resources can also answer questions before a sales conversation. Consider publishing practical guides, product explanations, case studies, or responses to common customer concerns. These pages show how your company thinks and give visitors something more valuable than a list of features.
Publish Content That Demonstrates Expertise
A steady flow of relevant content can help a brand build familiarity over time. Choose topics that connect your expertise with the real challenges your audience faces. For example, a cybersecurity company might explain how small teams can improve account security, while a software provider could share advice on choosing or implementing a tool.
Each article should have a clear purpose. It might explain a complex concept, offer a useful process, or help readers compare possible approaches. Avoid publishing only to fill a schedule; practical, well-organized information is more likely to earn attention and trust.
Reach New Readers Through Guest Articles
Publishing on relevant industry websites can introduce your ideas to readers who may not yet know your brand. The strongest guest articles are written for the publication’s audience first. They offer a genuine takeaway, fit the site’s subject, and mention your company only when it adds context.
Finding suitable outlets takes research. Look for websites whose readers match your intended audience, whose content is current, and whose editorial standards are clear. A resource such as iCopify’s technology listings can help you explore websites and blogs that accept technology guest articles. Treat a directory as a starting point: review each publication, its audience, and its submission guidelines before pitching.
Relevance is more important than a large number of placements. An article on a respected site that reaches the right readers may be more useful than several posts on unrelated websites. Focus on useful contributions and long-term credibility rather than quick results.
Build a Manageable Content Workflow
Consistent publishing involves more than writing. A typical workflow may include research, drafting, editing, graphics, proofreading, and outreach. Small teams can find it difficult to handle every task while also developing their product and serving customers.
Start by identifying the parts of the process that need extra support. You might need help with technical writing, illustrations, video, or campaign planning. A freelance marketplace such as Osdire lets buyers find freelancers across categories including programming, design, writing, video, and marketing. Before placing an order, define the scope, deadline, and expected deliverables. Clear instructions and review stages help both sides work toward the same result.
Keep ownership of your brand voice, even when other people contribute. Share examples of your preferred tone, explain the audience, and provide accurate product information. Review completed work for accuracy and consistency before it is published.
Measure What Is Working
Online visibility is not only about traffic. Consider whether your content is reaching the people you want to reach and whether it helps them take a meaningful next step. Depending on your goals, useful measures may include qualified inquiries, newsletter sign-ups, demo requests, or engagement with specific resources.
Look for patterns rather than reacting to one unusually successful or quiet week. If readers spend time with a particular topic, explore related questions. If a page attracts visitors but does not explain your offer clearly, improve the page before simply sending more traffic to it.
FAQs
How often should a technology business publish content?
Choose a schedule your team can maintain without sacrificing quality. A useful, well-edited article published regularly is more valuable than a frequent stream of rushed posts.
What makes a good guest article topic?
A good topic addresses a real question for the host publication’s readers and connects naturally to your expertise. It should offer value even to someone who never becomes a customer.
Should a small tech company hire freelancers?
Freelancers can help with specific tasks when internal time or skills are limited. Set clear requirements, agree on deadlines, and review the work before using it.
Conclusion
A stronger online presence grows from clear communication and useful work. Explain your value, make your website helpful, publish content with a purpose, and choose publishing opportunities that reach relevant readers. With a realistic workflow and regular review, technology brands can build visibility and trust without losing focus on the people they serve.
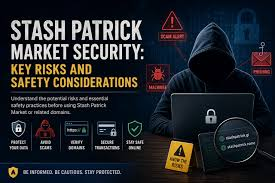
The dark web has become one of the most widely discussed areas of internet security. It is often associated with anonymous communication, privacy technologies, cybercrime forums, and underground marketplaces. stash patrick Within discussions about illicit payment-card markets, names such as Stash Patrick may appear as examples of the broader underground economy.
Understanding dark web marketplace access is useful from a cybersecurity and awareness perspective. However, it is important to distinguish between researching these environments and participating in stashpatrick.cc illegal activity. The purpose of examining names such as Stash Patrick is not to provide instructions for accessing or using illicit marketplaces, but to understand the risks these ecosystems create for consumers, businesses, and financial institutions.
What Is the Dark Web?
The dark web generally refers to online services that are not directly accessible through conventional search engines and that rely on specialized privacy-oriented technologies.
It is important to remember that privacy technology itself is not inherently criminal. Journalists, researchers, activists, and people living under restrictive regimes may use privacy tools for legitimate reasons.
The security concerns arise when anonymous environments are used to support illegal activities. Underground marketplaces can become places where stolen credentials, compromised payment information, malicious software, and other illicit services are advertised or exchanged.
Understanding Stash Patrick
Stash Patrick may be referenced in discussions concerning underground payment-card marketplaces. In this context, it should be viewed as part of a broader cybersecurity issue rather than as a conventional online financial service.
Underground marketplaces can change names, domains, infrastructure, and operating structures frequently. This makes individual marketplace identities less important than the underlying security problem.
For cybersecurity professionals, the key questions involve how financial information becomes compromised, how stolen information is circulated, and how organizations can prevent or detect its misuse.
Why Dark Web Markets Attract Attention
Underground markets can attract attention because they create an appearance of organized commerce.
Some illicit platforms have historically attempted to imitate legitimate e-commerce features such as listings, seller profiles, reputation systems, messaging functions, and payment mechanisms. This organization can make criminal activity appear more structured than it actually is.
For users, however, such environments carry substantial risks. There may be no reliable consumer protection, no trustworthy dispute-resolution process, and no assurance that advertised information is authentic.
A person interacting with an illicit marketplace may also become a target for scams, phishing, malware, or identity theft.
How Stolen Payment Information Reaches Underground Markets
Payment-card information can be compromised in many ways before it appears in criminal ecosystems.
Phishing is a major source of stolen credentials. Attackers may impersonate banks, retailers, payment companies, or other trusted organizations to convince victims to disclose sensitive information.
Malware can also collect information from compromised devices. Certain forms of malicious software are designed to steal credentials or other sensitive data.
Data breaches represent another important source. When organizations fail to properly secure databases, applications, or third-party systems, attackers may obtain information belonging to customers.
Social engineering is another pathway. Criminals may manipulate employees or consumers into revealing information that should remain confidential.
These different attack methods demonstrate that underground marketplaces are often only one part of a much larger criminal ecosystem.
The Risks of Marketplace Access
People sometimes assume that the main risk associated with dark web marketplaces is simply the illegal nature of the products being offered. In reality, the cybersecurity risks can be much broader.
Illicit platforms may attempt to collect visitors’ credentials or personal information. Malicious files or deceptive links can expose devices to security threats.
Scammers may also advertise information that does not actually exist. Someone seeking unauthorized financial information can lose money while simultaneously exposing personal details.
There is also a serious legal and ethical dimension. Using stolen payment information can directly harm victims and may result in criminal or civil consequences.
For these reasons, users should avoid attempting to purchase, test, or use stolen financial information.
Protecting Consumers From Dark Web-Related Threats
Consumers can take several practical steps to reduce their exposure to threats associated with compromised information.
Using unique passwords for important accounts is a fundamental precaution. Password reuse allows attackers to potentially move from one compromised service to another.
Multi-factor authentication provides another important layer. If a password is stolen, an attacker may still be blocked by an additional verification requirement.
Consumers should also monitor financial accounts regularly. Transaction alerts can provide early warnings about unauthorized activity.
If suspicious activity is identified, users should contact their financial institution through an official channel rather than responding to messages or links supplied by unknown parties.
The Importance of Phishing Awareness
Many security incidents begin with seemingly ordinary messages.
A fraudulent email or text message may claim that a payment failed, an account requires verification, or suspicious activity has been detected. The objective is often to create urgency and encourage the recipient to click a link or provide information.
Users should treat unexpected requests for passwords, payment details, authentication codes, or identity documents with caution.
Instead of following links in suspicious messages, users should open their financial institution’s official application or navigate to a trusted website independently.
Lessons for Businesses
Businesses can learn important lessons from underground payment-card ecosystems.
Organizations should protect sensitive information using layered security controls. Encryption, access management, network segmentation, endpoint security, vulnerability management, and continuous monitoring can help reduce the likelihood of compromise.
Businesses should also minimize the amount of sensitive information they store. Data that is unnecessary for business operations can create unnecessary security exposure.
Employee education is equally important. Staff members should understand phishing, social engineering, password security, and procedures for reporting suspicious activity.
Threat Intelligence and Defensive Research
Cybersecurity professionals may monitor threat intelligence sources to understand emerging underground-market activity.
This type of research can help organizations identify compromised credentials, understand new attack techniques, and determine whether their information may have appeared in criminal ecosystems.
Defensive research should be conducted through authorized and responsible methods. Security teams do not need to participate in criminal transactions to learn about threats.
The objective is to gather information that improves detection, prevention, and incident response.
The Future of Underground Markets
Underground markets are likely to continue evolving alongside technology.
Criminal groups may adopt automation, artificial intelligence, encrypted communication, and increasingly sophisticated social-engineering techniques. At the same time, financial institutions, cybersecurity companies, and law enforcement agencies are improving their ability to identify suspicious behavior.
Artificial intelligence may become particularly important. Defensive systems can analyze large quantities of transactions and security events to identify unusual patterns.
However, attackers may also use automation to scale fraudulent campaigns. This means cybersecurity will remain a continuing contest between evolving attack methods and defensive innovation.
Responsible Cybersecurity Awareness
It is important to discuss dark web marketplaces without unintentionally encouraging participation.
Security education should focus on understanding threats, recognizing warning signs, protecting accounts, and responding effectively to incidents.
For researchers, journalists, and cybersecurity professionals, responsible analysis can provide useful insight into how criminal ecosystems operate without facilitating illegal activity.
For ordinary users, the most important takeaway is that suspicious financial services should never be treated as convenient alternatives to legitimate providers.
Conclusion
Stash Patrick can be considered within the broader discussion of dark web marketplace activity and underground payment-card ecosystems. However, individual marketplace names and domains are less important than the security issues they represent.
Unauthorized payment-card markets can expose consumers to fraud, identity theft, malware, scams, and legal risks. They also demonstrate how stolen information can move through complex criminal networks after an initial compromise.
Consumers can reduce their exposure by using strong unique passwords, enabling multi-factor authentication, monitoring financial accounts, recognizing phishing attempts, and obtaining financial services through legitimate providers.
Businesses can strengthen their defenses through layered security, data minimization, employee education, threat intelligence, and effective incident-response planning.
Ultimately, understanding dark web marketplaces should serve a defensive purpose. By studying the risks without facilitating criminal access, cybersecurity professionals and everyday users can develop better strategies for protecting digital identities, payment information, and financial systems.
The underground side of the internet has long been a subject of interest for cybersecurity researchers, financial institutions, and law-enforcement agencies. Among the most concerning areas are online communities and marketplaces associated with stolen payment information. Discussions surrounding names such as bclub and the domain bclub.tk have appeared in this broader context, particularly in connection with references to “dumps” and CVV2-related data.
These terms can sound highly technical, but they point toward a much larger cybersecurity problem: the unauthorized acquisition, circulation, and potential misuse of financial information.
It is important to approach discussions about specific websites carefully. Online reports may contain outdated information, unsupported claims, or references to infrastructure that has changed over time. A domain name by itself does not establish who operates a service, what its current activities are, or whether every claim made about it is accurate.
With that distinction in mind, examining why Bclub.tk became associated with discussions about dumps and CVV2 information provides useful insight into payment-card security, cybercrime ecosystems, and the risks faced by consumers and businesses.
What Does “Bclub” Refer To?
Bclub is a name that has appeared in online discussions involving underground financial-data marketplaces and payment-card information.
The domain bclub.tk has likewise been mentioned in discussions surrounding this subject. However, publicly available references do not necessarily provide a complete or independently verified picture of the website’s ownership, infrastructure, history, or current status.
This is an important consideration when researching cybersecurity topics. Online discussions often combine technical observations with speculation, and information about underground services can change rapidly.
Rather than treating every claim about Bclub as established fact, it is more useful to examine the cybersecurity concepts that have made the name noteworthy.
What Are “Dumps”?
In cybersecurity and payment-fraud terminology, “dumps” generally refers to stolen data derived from the information encoded on a payment card’s magnetic stripe.
Such information can be sensitive because payment-card credentials are connected to financial accounts. If obtained without authorization, they can potentially be used in fraudulent activity.
The term is therefore frequently encountered in discussions of payment-card breaches and underground cybercrime.
From a defensive perspective, the existence of markets dealing in this type of information highlights the importance of protecting payment systems throughout their entire lifecycle.
Businesses must secure point-of-sale environments, payment infrastructure, employee access, databases, and third-party services. Consumers, meanwhile, need to monitor accounts and respond quickly when suspicious activity occurs.
What Is CVV2?
CVV2 is a security code associated with many payment cards and is commonly used as an additional verification element for certain card-not-present transactions.
For many cards, the code consists of three digits printed on the card. Some card networks use different terminology or formats.
CVV2 is sensitive authentication information and should not be treated as ordinary personal information.
However, it is also important to understand what CVV2 does not mean. Possession of a CVV2 does not automatically guarantee that a transaction will be approved. Payment systems can use numerous other controls, including issuer authorization, transaction monitoring, authentication mechanisms, and fraud-detection systems.
Under payment-card security requirements, sensitive authentication data such as card verification codes must not be retained after authorization.
Why Dumps and CVV2 Became Recurring Topics
The combination of stolen card information and authentication-related data is a major concern because criminals may seek multiple pieces of information when attempting financial fraud.
This helps explain why terms such as “dumps” and “CVV2” frequently appear together in discussions about underground payment-card activity.
However, the presence of these terms in online discussions should not be interpreted as proof that a particular website currently possesses, sells, or distributes specific data.
Cybersecurity researchers often track terminology, domains, infrastructure, and criminal advertisements to understand emerging threats. Their observations may subsequently be repeated across blogs, forums, and social media, sometimes without the original context.
As a result, readers should distinguish between documented cybersecurity research, reported allegations, and unverified online claims.
How Payment Card Information Can Be Compromised
The risks discussed around underground card-data marketplaces begin much earlier than a marketplace itself.
Payment information can be compromised through several different attack methods.
Data Breaches
Attackers may target businesses that store or process customer information. A successful breach can expose large amounts of data, depending on the systems involved.
Phishing
Fraudsters may use fake emails, text messages, or websites to persuade people to disclose payment or account information.
Malware
Malicious software can compromise computers and mobile devices and potentially expose sensitive information.
Point-of-Sale Attacks
Retail payment systems can become targets when attackers discover weaknesses in software, networks, or administrative controls.
Social Engineering
Attackers may manipulate employees or customers into revealing information or performing actions that weaken security.
These pathways demonstrate that protecting financial data requires more than securing a single website or database.
The Risks for Consumers
Payment-card data exposure can have serious consequences for individuals.
The most immediate risk is unauthorized financial activity. A compromised card may need to be blocked or replaced, and suspicious transactions may need to be disputed.
There can also be broader privacy concerns when payment information is exposed alongside names, addresses, email accounts, or other identifying details.
Consumers may subsequently become targets of phishing attempts designed around information obtained from previous incidents.
The practical consequences can include:
- Unexpected transactions
- Card replacement and account disruption
- Time spent resolving fraudulent activity
- Increased phishing attempts
- Privacy concerns
- Potential identity-related fraud
For this reason, consumers should regularly monitor their financial accounts and take unexpected security notifications seriously.
The Risks for Businesses
Businesses face their own set of challenges when payment information is compromised.
A security incident can result in fraudulent transactions, chargebacks, investigation costs, customer complaints, and reputational consequences.
Organizations may also have regulatory, contractual, or legal obligations depending on the nature of the incident and the jurisdictions involved.
Businesses that handle payment information should therefore adopt layered security measures rather than relying on a single defense.
These can include strong access controls, network segmentation, vulnerability management, encryption where appropriate, secure payment technologies, employee training, monitoring, and incident-response procedures.
The Importance of PCI DSS
The Payment Card Industry Data Security Standard, commonly known as PCI DSS, provides security requirements for organizations involved in storing, processing, or transmitting payment-card information.
The standard addresses areas including access management, system security, vulnerability management, monitoring, and protection of payment data.
One particularly important principle is minimizing the amount of sensitive payment information retained by an organization.
Sensitive authentication data, including card verification codes such as CVV2, must not be stored after authorization.
Organizations can also reduce risk by using tokenization and appropriately designed payment-processing systems that limit exposure to raw card information.
How Consumers Can Reduce Their Risk
Individuals do not need to understand underground marketplaces to improve their payment security.
Several basic practices can make a meaningful difference.
Monitor accounts regularly. Review bank and card transactions and report unfamiliar activity promptly.
Enable transaction notifications. Alerts can help identify unexpected activity quickly.
Use multi-factor authentication. MFA adds another layer of protection to banking, email, and other important accounts.
Use unique passwords. Password reuse can allow one compromised account to affect multiple services.
Be cautious with unexpected messages. Banks and legitimate businesses generally provide official channels for account management. Avoid entering sensitive information through suspicious links.
Keep devices updated. Security updates can address known vulnerabilities.
Contact your financial institution after suspected exposure. The card issuer can provide guidance about blocking or replacing a compromised card.
Why Online Claims Require Careful Verification
One of the most important lessons from discussions surrounding Bclub.tk is the need to evaluate online information critically.
Underground websites can disappear, change domains, migrate infrastructure, or become inactive. At the same time, third-party articles may continue to repeat information long after circumstances have changed.
Readers should therefore look for information from reputable cybersecurity companies, financial institutions, government agencies, and established security researchers.
It is also important to avoid treating screenshots, forum posts, advertisements, or anonymous claims as definitive evidence.
Responsible cybersecurity reporting distinguishes clearly between what has been verified and what remains alleged or uncertain.
The Broader Cybersecurity Lesson
The discussion surrounding Bclub and payment-card terminology reflects a much larger evolution in cybercrime.
Financial information has become an attractive target because digital commerce depends heavily on electronic transactions.
At the same time, payment networks have developed increasingly sophisticated defenses. Banks and payment processors use fraud monitoring, authentication technologies, transaction analysis, and other controls to identify suspicious activity.
This creates an ongoing cycle in which defensive technologies evolve alongside new attack techniques.
For consumers and businesses, the most useful response is not to understand the mechanics of underground marketplaces but to strengthen the security practices that make stolen information harder to obtain and harder to misuse.
Conclusion
Bclub.tk has appeared in online discussions connecting the Bclub name with payment-card data, “dumps,” and CVV2-related terminology. Those discussions form part of a wider cybersecurity landscape involving unauthorized financial information and online fraud.
Specific claims about the website, its operators, or its activities should be independently verified, particularly because online information can be incomplete, outdated, or speculative.
The broader security issues are nevertheless important. Payment-card information can be compromised through data breaches, phishing, malware, social engineering, and weaknesses in payment infrastructure. When sensitive information is exposed, consumers and businesses can face financial, operational, and privacy-related consequences.
Strong payment security therefore requires multiple layers of protection. Consumers should monitor accounts, use strong authentication, protect sensitive information, and respond quickly to suspicious activity. Businesses should minimize sensitive-data retention, follow applicable security standards, and maintain effective security and incident-response programs.
Ultimately, discussions about Bclub and similar names are most useful when they encourage greater cybersecurity awareness. Understanding the risks associated with compromised payment information can help individuals and organizations make safer decisions without becoming involved with the underground activities themselves.
Disclaimer: This article is for educational and defensive cybersecurity awareness. It does not endorse Bclub, bclub.tk, card-data marketplaces, carding, or the acquisition, sale, or use of unauthorized payment information. Specific claims about websites or online services should be independently verified using reliable sources.
How Tech Brands Can Build a Stronger Online Presence

Stash Patrick: A Look at Dark Web Marketplace Access
Inside Bclub: How Bclub.tk Became Associated With Dumps and CVV2 Discussions
Daman Game Download: Everything You Need to Know
Daman Game: Complete Guide to Using Your Account
Major Decisions to Make Before Launching a New Local Enterprise
1000+ Great Instagram Bio For Boys – Stylish & Attitude Bio
1500+ Perfect Instagram Bio For Hindu
Krishna Bio For Instagram
500+ Great Mahakal Bio For Instagram 2024
Hanuman Ji Bio For Instagram
900+ Perfect Facebook Bio For Boys 2024 – Attitude Bio
-
Instagram Bio Ideas3 years ago
1000+ Great Instagram Bio For Boys – Stylish & Attitude Bio
-
Instagram Bio Ideas2 years ago
1500+ Perfect Instagram Bio For Hindu
-
Instagram Bio Ideas2 years ago
Krishna Bio For Instagram
-
Instagram Bio Ideas3 years ago
500+ Great Mahakal Bio For Instagram 2024
-
Instagram Bio Ideas2 years ago
Hanuman Ji Bio For Instagram
-
Facebook Bio Ideas3 years ago
900+ Perfect Facebook Bio For Boys 2024 – Attitude Bio
-
 Instagram Bio Ideas3 years ago
250+ Best Music Bio For Instagram 2024 – Music Lover Bio
-
 Facebook Bio Ideas2 years ago
1200+ Best Facebook bio ideas 2024 – Stylish, Short and Unique FB bio